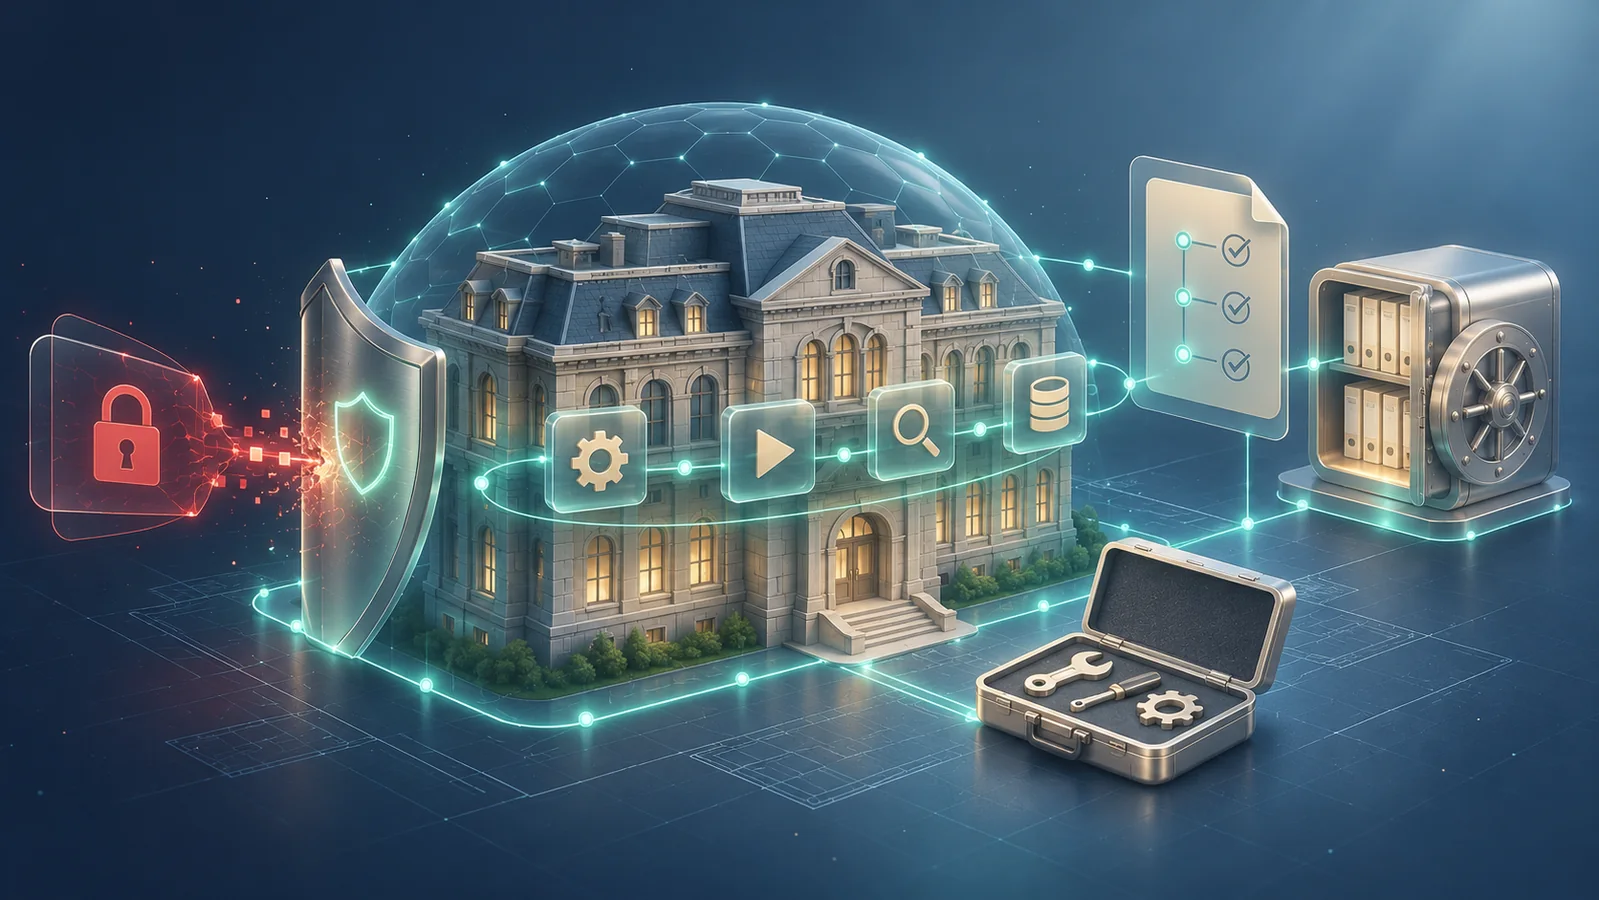
This ransomware defence strategy uses immutability, timestamping and traceability to limit damage and demonstrate NIS2 compliance.
Evidentiary governance vs declarative compliance
Prior to NIS2, compliance was declarative: the mere existence of tools sufficed as proof. Under NIS2, every decision, action, and control must be demonstrated: who approved what, when, and within which scope. Accountability, historically delegated to technical teams, now ascends to executive management, who must justify the evidence presented.
Evidence required in the event of ransomware
| Evidence | Actionable format |
|---|---|
| Risk analysis | Signed report, qualified timestamp, hash recorded in immutable register |
| Approved backup policy | GPG-signed Git commit with policy-backup tag |
| Critical asset inventory | JSON export from CMDB, SHA-256 hash, stored in S3 Object Lock |
| Backup logs | Append-only stream to WORM, each line timestamped and hashed |
| Ransomware incident report | Electronically signed PDF, timestamped |
Immutability as a trust mechanism
- WORM: media permitting no overwriting after commit;
- append-only logs: new entries added only at the end;
- SHA-256 or SHA-3 fingerprints: unique hash upon creation;
- Merkle chaining: each entry incorporates the previous hash;
- Signed Git + GPG versioning with timestamping;
- Qualified timestamping via certified service;
- Centralised SIEM audit logs with immutable replication.
Link to ransomware incident management
- minute-by-minute chronological reconstruction using immutable logs;
- verifiable active measures via timestamped snapshots of the detection system;
- documented decisions: signed crisis committee reports proving validation;
- regulatory notifications: certified copies, qualified timestamping;
- forensic analysis: disk image hash fingerprints compared against the registry.
Pragmatic implementation for SMEs and Mid-caps
- map applicable NIS2 obligations;
- define an evidence register (simple table or database);
- assign a data custodian per category;
- automate daily backups and their immutable recording;
- protect via append-only versioning, GPG signatures, and Legal Hold;
- regularly verify readability and integrity;
- test the audit trail by simulating an authority request.
What KARL delivers
KARL ensures that every document version and log is preserved as durable evidence: native immutability, precise timestamping, and full traceability. In the event of a ransomware attack, the organisation has immediate access to a healthy state for restoration and auditable proof to demonstrate risk management, without needing to rebuild the infrastructure.
Limitations that should not be overlooked
- immutability does not guarantee the accuracy of the source;
- GDPR conflict (right to erasure) vs NIS2 retention requirements requiring analysis;
- immutability is not a substitute for prevention.
Further reading
Further reading:
Read the Challenges article on KARL →