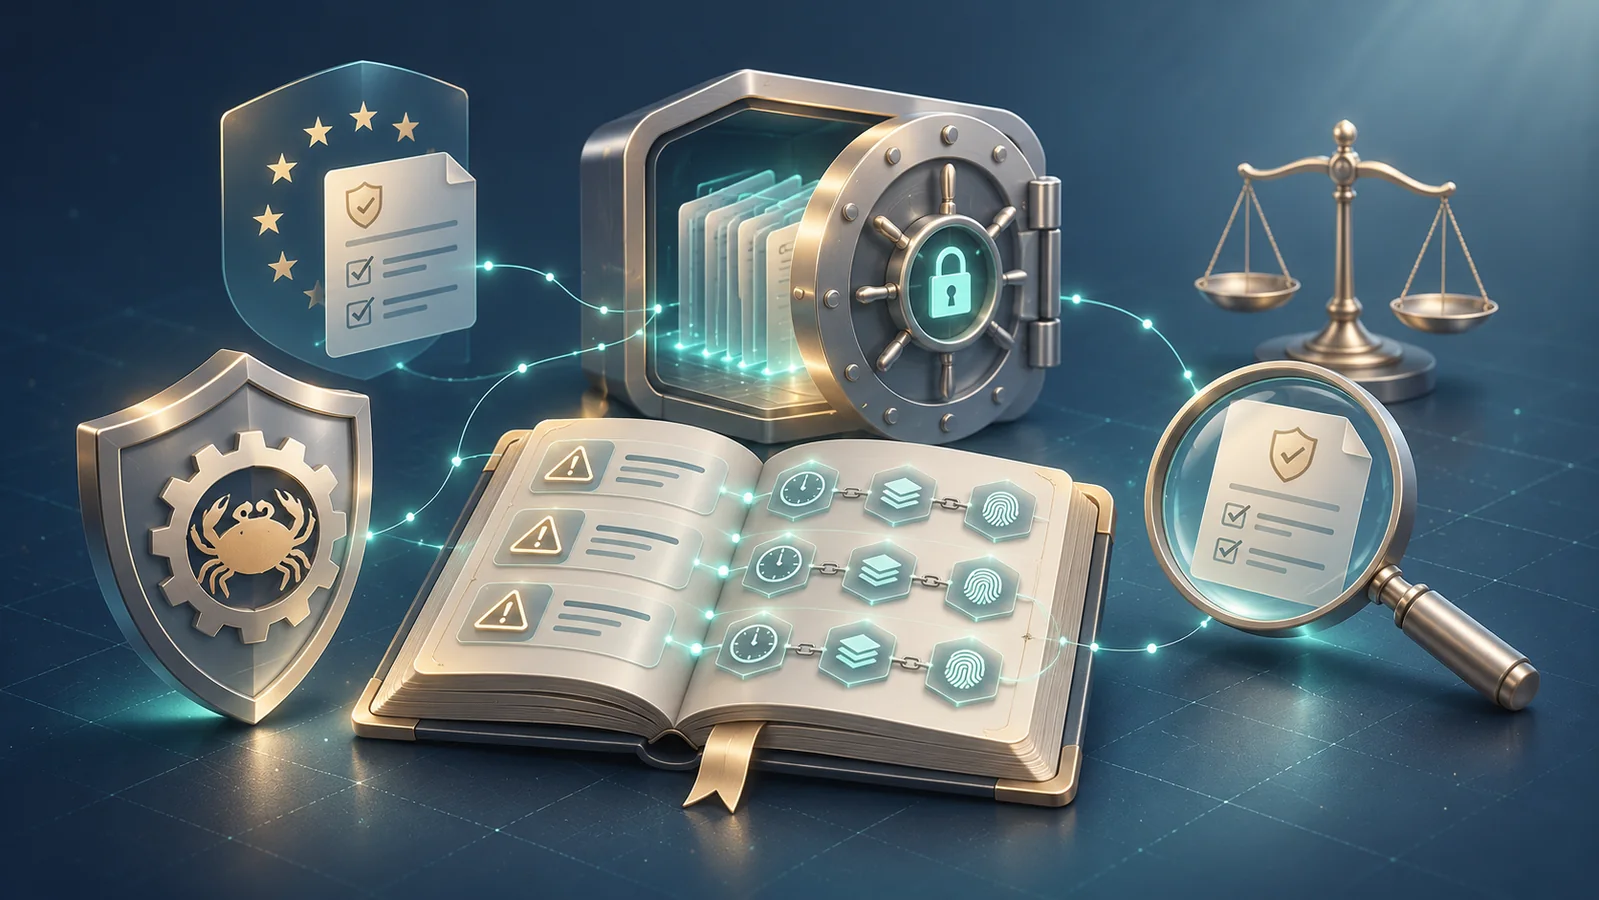
A behavioural detection system written in Rust produces alerts that are preserved as immutable legal evidence for NIS2.
Providing proof for every alert
- authenticity: identifiable and recognised source of information;
- integrity: content unmodified since creation;
- traceability: every step recorded;
- reliable timestamping: date and time securely sourced;
- attribution: actor or system that generated the data identified;
- contextualisation: document inserted into a described process;
- availability during the required period;
- long-term readability (PDF/A, signed JSON).
Chain of custody for an SSA alert
An SSA alert is generated by the Rust engine with metadata (IP source, account identity). Each alert carries a UUID, a timestamp and the identifier of the producing service. A call to the internal TSA obtains a signed timestamp. The SHA-256 hash of the full payload is stored in an immutable log. Writing is performed on a WORM layer or within an S3 Object Lock bucket in Compliance mode.
NIS2 evidence register - example
| Field | Example value |
|---|---|
| ID | Unique UUID v4 |
| Proof type | Behavioural alert |
| Source | Rust SSA Plugin |
| Format | Signed JSON |
| Timestamp | TSA Certificate |
| Hash | SHA-256 |
| Storage | S3 Object Lock |
| Retention | 7 years |
The register is maintained in a Git repository; any modification triggers a pull request validated by the DPO or the CISO.
Audit scenario: from detection to submission of evidence
An SSA alert is triggered and appears on the SOC dashboard. The CSIRT isolates the account, applies a patch, and logs the action in a ticket. Upon an audit request from an authority, a script extracts the event from the S3 bucket, verifies the hash, adds the TSA certificate, and packages everything into audit-package.zip containing the JSON, certificate, and evidence register.
Pragmatic implementation for SMEs and Mid-caps
- map NIS2 obligations in a requirement/evidence table;
- define an evidence register (simple tool: Git, immutable database);
- assign a lead for each category (alerts, backups, policies);
- specify source, frequency, format and duration;
- automate collection: the Rust plugin pushes directly to S3 with TSA signature;
- protect via strict ACLs, encryption at rest, and multi-zone replication.
Limitations not to be overlooked
- an immutable record may contain erroneous information: source quality is paramount;
- GDPR / NIS2 conflict requiring an impact analysis;
- immutability is not a substitute for prevention.
Further reading
Further reading:
Read the Challenges article on KARL →