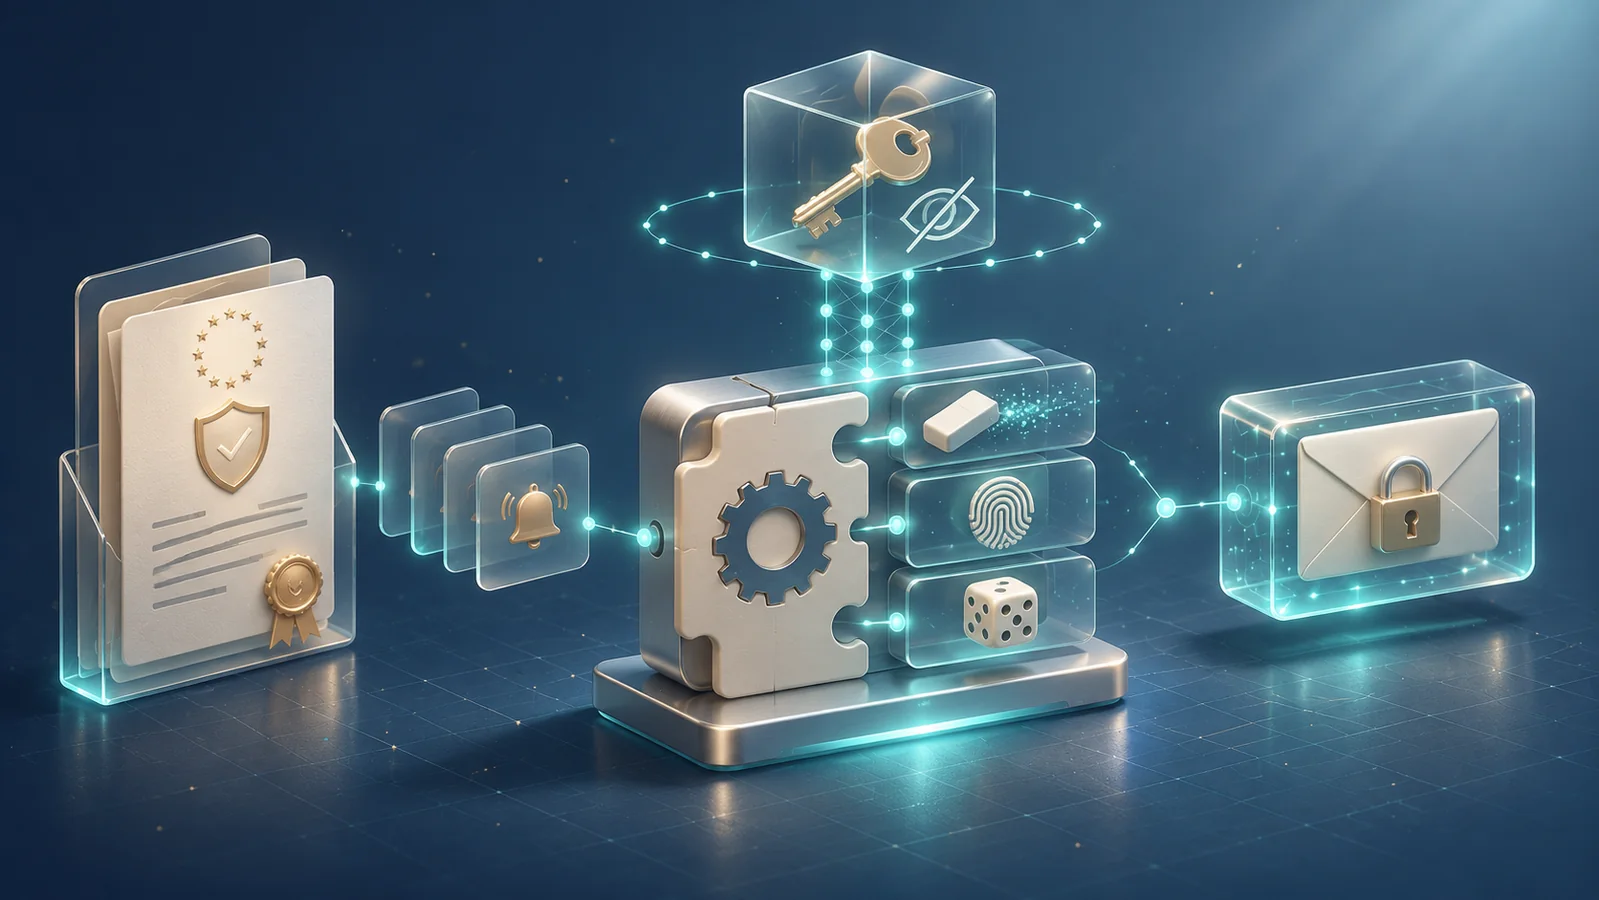
A Rust plugin can generate encrypted alerts and immutable, timestamped evidence to meet NIS2 requirements.
Proof within the context of an alerting plugin
- authenticity: alert source (Rust service) identified via certificate or signature;
- integrity: encrypted payload cannot be modified without altering the SHA-256 hash and signature;
- traceability: each alert carries a unique UUID v4, timestamped by TSA;
- reliable timestamping: certified timestamp preventing any backdating disputes;
- attribution: IAM identifier or certificate of the service generating the alert recorded in the log.
Cryptographic primitives
| Primitive | NIS2 role and benefit |
|---|---|
| zeroize (v2) | Immediately overwrites variables containing keys in memory |
| sha2 (RustCrypto) | Implements FIPS 180-4 for SHA-256 hash (integrity + identifier) |
| uuid v4 | Generates an RFC 4122 identifier with statistical uniqueness |
| ring / ed25519-dalek | Fast and robust EdDSA digital signature |
Rust’s ownership system prevents unnecessary copies of the key, reducing the attack surface.
What an auditor will seek to verify
- each alert possesses a unique UUID v4 and a TSA timestamp;
- the encrypted payload is accompanied by a verifiable SHA-256 signature;
- private keys are never persisted to disk and are erased from RAM (zeroize);
- reception logs are stored as append-only with strict IAM;
- the chain of custody complies with the defined retention policy.
Chain of custody for an encrypted alert
The Rust plugin detects an anomaly, generates a UUID v4, and retrieves metadata (source IP, SHA-256 hash of the suspect file). The service identifier (service_id) is added to the message. The payload is hashed prior to encryption, and the hash is sent to the TSA. The SHA-256 of the encrypted payload is stored in the S3 object metadata. The signed JSON-LD object is uploaded to an Object Lock bucket (Compliance) with tags retention=7y and type=alert.
CNIL audit scenario
The CNIL sends a request to the DPO requesting unauthorised access alerts from 1st to 28th February 2024. The DPO executes a script that queries the S3 bucket, retrieves the JSON-LD files, recomputes the SHA-256 hashes, verifies the TSA signature, and then creates audit_feb2024.zip.sig. The DPO transmits the zip via an encrypted channel; the CNIL validates the signatures using the service's public certificate and confirms that the alerts are immutable, timestamped, and correctly classified.
Pragmatic implementation for SMEs and Mid-caps
- map NIS2, GDPR, and ISO 27001 obligations;
- define a proof register in a Git repository (JSON) automated via cargo-run;
- assign a data custodian per alert category;
- specify signed JSON-LD format, 7-year retention, S3 Object Lock;
- automate collection via a Rust plugin hook;
- publish each alert with its trace immediately in the register.
Limitations to consider
- immutability does not eliminate a false alert generated at the source;
- primacy of source quality;
- local vs qualified timestamping: differing legal weight;
- costs for SMEs can be significant.
Find out more
Find out more:
Read the Challenges article on KARL →