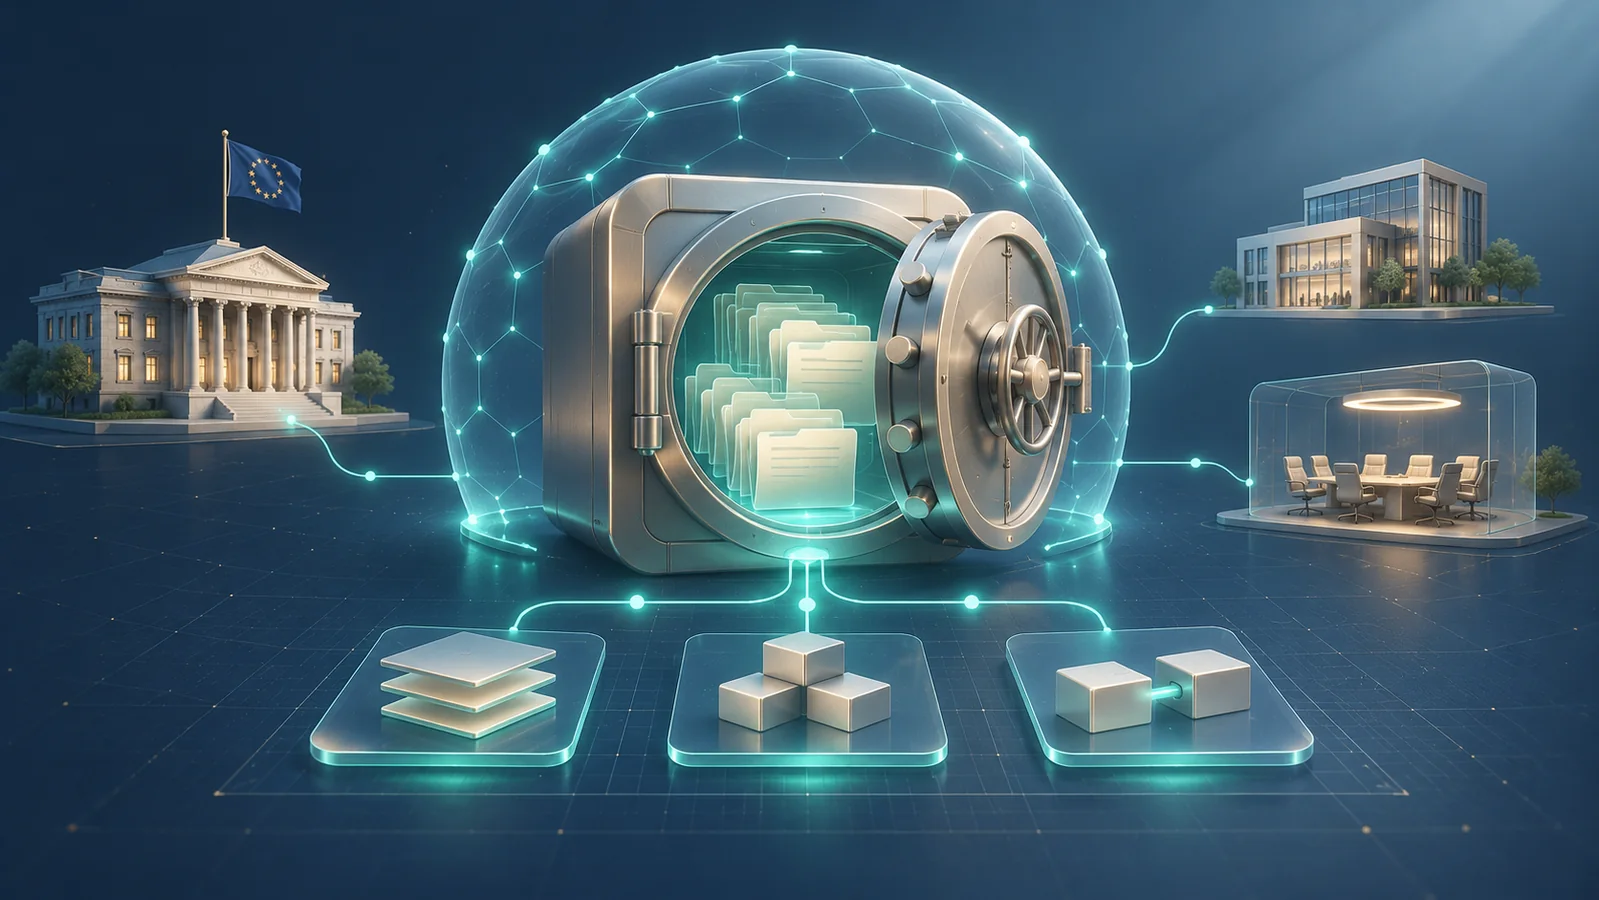
For years, digital sovereignty was treated as a political issue. It has now become an operational matter: where is the data stored, who can access it, under which jurisdiction, and according to what technical guarantees?
A subject that now affects all organisations
- administrations that must guarantee non-accessibility by foreign jurisdictions;
- healthcare providers subject to HDS;
- financial operators subject to DORA;
- essential entities as defined by NIS2;
- exporting mid-caps (ETIs), subject to increasingly stringent contractual constraints.
The false comfort of hyperscale platforms
Storing data with a global cloud provider can create a sense of security. But it guarantees neither legal sovereignty nor control over data history or the ability to reproduce a past state.
Sovereignty is not merely a question of location: it is also a question of control.
The pillars of truly controlled data
- the choice of S3 storage (sovereign, hybrid, or cloud);
- encryption managed by the organisation;
- provider-independent historisation;
- unrestricted data export;
- the absence of vendor lock-in.
KARL and practical sovereignty
KARL is designed to operate on the leading S3 implementations — whether sovereign, on-premise, or international cloud — without relying on an intermediate database or a third-party service.
This approach allows each organisation to freely choose its infrastructure while maintaining the same level of traceability, immutability, and resilience.
Sovereignty becomes what it should have always been: a choice, not a constraint.
Find out more
Find out more:
Read the Challenges article on KARL →