How to design a decoupled audit microservice using S3 Object Lock to create an immutable chain of custody that meets NIS2 requirements?
An audit that no longer holds up before the CNIL
A French insurance company uses a monolithic Java engine writing access logs to a shared disk. During a NIS2 audit, only a CSV export from the previous day is available, lacking both hashes and certified timestamps. The CNIL concludes that this evidence guarantees neither the authenticity nor the integrity of the events.
Providing proof within the microservices model
| Quality | Contribution to the microservices architecture |
|---|---|
| Authenticity | Identified producer service (UUID v4, Docker image hash) |
| Integrity | Each log SHA-256 hashed prior to storage |
| Traceability | trace_id propagated across the service chain |
| Timestamping | Hash sent to a TSA (RFC 3161), signed certificate returned |
| Attribution | Service name, Git commit, operator ID in the metadata |
| Availability | S3 Object Lock with retention ≥ 7 years |
Rust pattern using aws-sdk-s3
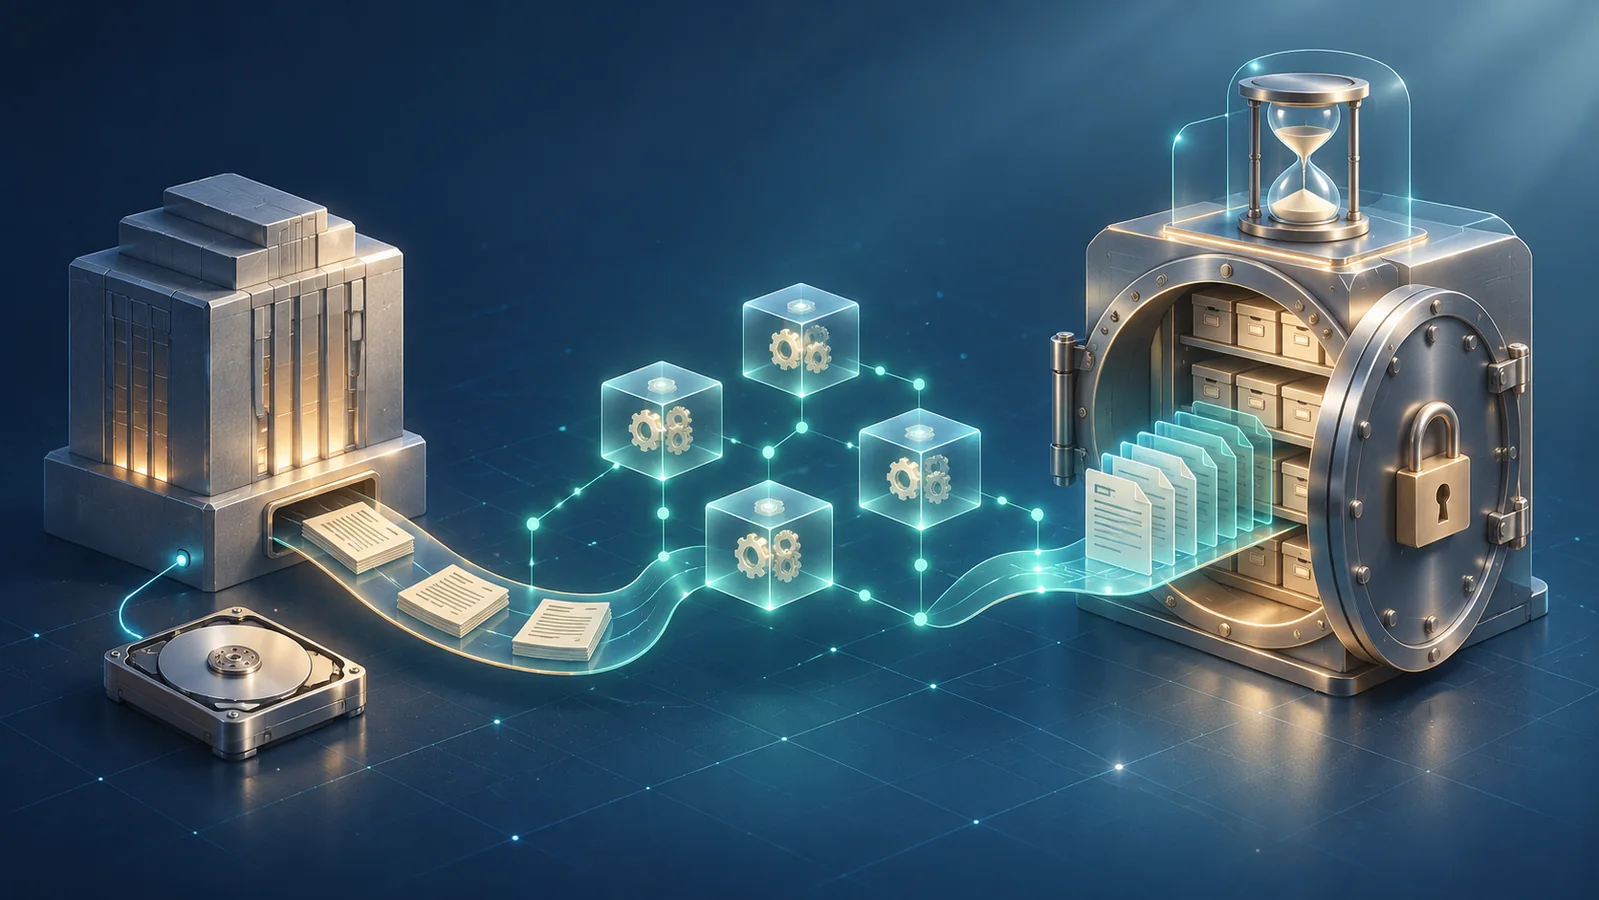
The aws-sdk-s3 SDK for Rust enables a stateless implementation for microservices: S3 client creation, construction of the audit payload (UUID v4, UTC timestamp, action, user, Git commit), SHA-256 hash calculation, transmission to a TSA, package assembly, and subsequent upload in Object Lock Compliance mode with 7-year retention.
What an auditor will seek to verify
- each event has a unique UUID event_id;
- the SHA-256 hash of the payload is signed by a certified TSA;
- the S3 object was created in Object Lock (immutable) mode;
- metadata includes the service version (git_commit);
- the documented retention policy is enforced.
File audit chain of custody
- the file_audit microservice intercepts every file access (open, read, write);
- addition of service_uuid, Git commit and request_id to the payload;
- SHA-256 hashing followed by transmission to the TSA;
- complete JSON-LD object uploaded to S3 Object Lock (retention=7y);
- daily verification: hash recalculation and comparison;
- read-only interface exposing metadata and TSA certificate;
- audit export as a signed ZIP archive.
What KARL delivers
KARL natively provides immutability, versioning, and traceability on S3 storage without relying on an intermediate database. The chain of custody becomes a property of the storage itself, significantly accelerating the migration from an audit monolith to a NIS2-compliant microservices model.
Limitations not to be overlooked
- pseudo-immutability possible if the source is compromised;
- GDPR vs NIS2 conflict requiring Legal Hold analysis;
- local vs qualified timestamping: only the latter has legal validity;
- significant cost of WORM and TSA services for SMEs.
Further reading
Related links:
Read the Challenges article on KARL →