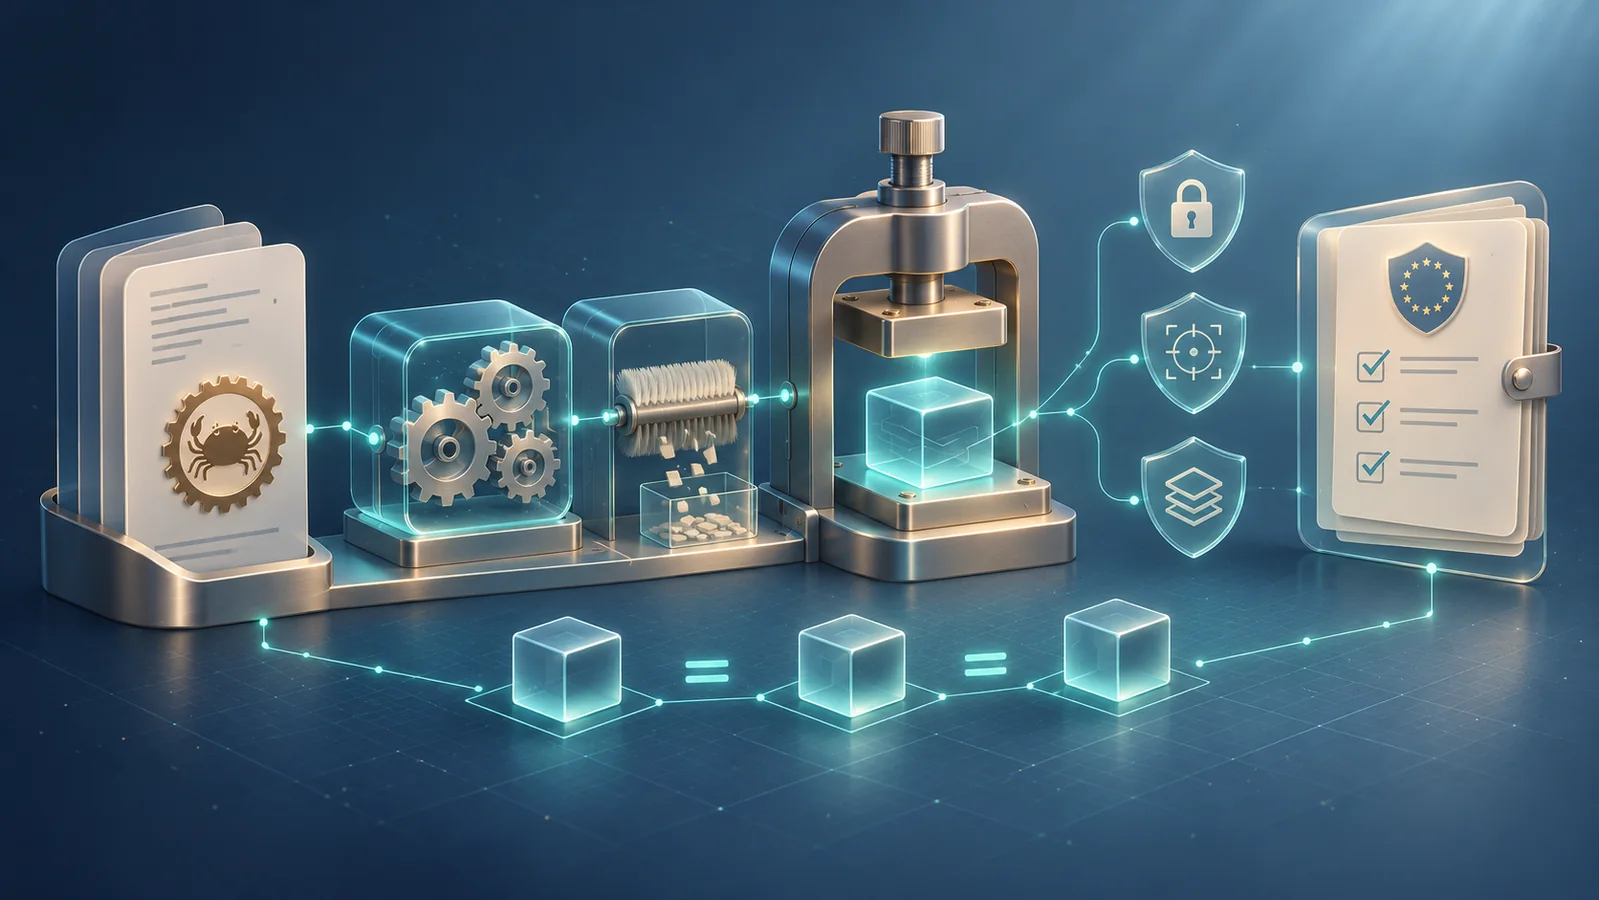
Rust release profiles can produce deterministic, hashed and timestamped binaries that provide evidence for NIS2 audits and incident response.
Proof required for each measure
NIS2 requires traceability: every security action must be recorded with a reliable timestamp. Management must also demonstrate that the measures were implemented. No specific technology is prescribed, but the evidence must be authentic, intact and verifiable.
Providing proof for a Rust binary
- authenticity: signed hash attests that the binary originates from the referenced Git repository (commit SHA);
- integrity: any alteration changes the hash; the TSA signature makes such modification detectable;
- traceability: release-lto-strip profile name, rustc version, crate version number;
- qualified timestamping: TSA service (RFC 3161) signs the hash;
- attribution: CI/CD logs include the pipeline ID, operator, and Git commit.
Configuration of the release-lto-strip profile
| Cargo.toml Option | Effect |
|---|---|
| opt-level = "z" | Maximum size optimisation |
| debug = false | No embedded debug symbols |
| strip = true | Symbol stripping (Rust 1.60+) |
| lto = true | Link-Time Optimisation enabled |
| codegen-units = 1 | Single code unit for determinism |
| panic = "abort" | Reduced panic handling code |
| incremental = false | Disables non-reproducible intermediate artefacts |
Chain of custody for a binary
CI Pipeline: cargo build --release using the release-lto-strip profile. The manifest includes the Git commit, crate version, and compiler flags. The binary is SHA-256 hashed and then sent to the TSA, which returns a certificate. The SHA-256 + certificate form a complete JSON-LD object uploaded to an S3 Object Lock bucket (retention=7y tag). A daily job verifies integrity.
Link with forensic incident management
The signed hash allows for the immediate identification of the binary executed during an intrusion. The hashing chain (binary → hash → TSA certificate) provides an immutable timeline for forensic teams. Each patch generates a new binary with a different hash, proving that the update was effectively applied. Notifications to authorities include the TSA certificate, ensuring the non-repudiation of dates.
Limitations not to be overlooked
- potential false immutability if hash generation is flawed;
- source quality is paramount;
- local vs qualified timestamping: differing legal weight;
- costs for SMEs can be significant;
- immutability ≠ prevention: early detection remains indispensable.
Further reading
To learn more:
Read the Challenges article on KARL →